# /home
Infosec Addict
Hi, there! My name is Brian, and I eat, drink, sleep, and breathe infosec and technology. I love to figure out how things work (digital, mechanical, or otherwise). I also love anything that goes FAST: cars, motorcycles, planes, and rockets (especially rockets!).
## Note: Redacted Information
Some information displayed (particularly in the Experience and Education sections) is redacted. Why is this? Well, the internet is a dangerous place. There are millions of malicious web-scraping bots and threat actors out there that are constantly dragging the internet for sensitive data. As a result: PII that isn't critical to this page has been redacted. You'll also find that the downloadable resume is redacted. Un-redacted versions of data will be provided only by request and after identity verification. Thank you for your understanding.
# Work Experience
**Security Consultant**\
\[Redacted Offensive Security]\
October 2022 - Present
**Owner & Lead Developer**\
Offworld Systems LLC\
September 2020 - January 2023
**Full Stack Developer**\
\[Redacted MSSP]\
August 2019 - October 2020
**Sr. Cyber Security Analyst**\
\[Redacted MSSP]\
February 2018 - August 2019
**Information Technology Support Specialist**\
\[Redacted University]\
February 2017 - January 2018
**Information Technology Support Technician**\
\[Redacted University]\
May 2016 - January 2018
**Help Desk Technician**\
\[Redacted University]\
January 2014 - April 2016
# Education
## BS Information Technology - Computer Security & Cryptography
\[Redacted University]
\[Location Redacted]
August 2012 - December 2016
BS Information Technology - Computer Security & Cryptography
# Certifications
* [OSCP](https://www.credly.com/badges/feb95537-81b9-4cf0-bbe4-b7a8d804d03d/linked_in_profile)
* [PNPT](https://www.credential.net/1474599d-ad39-461b-ab08-cddcf6fdded2#gs.8f4w1i)
* eLearn Security - EJPT (credential ID: EJPT-4509178)
* FCC - HAM Technician License (callsign: \[REDACTED])
# Books
Good for health... Ba-... Good for education too!
⚠️----🔜----⚠️
# Podcasts
Listen 'n learn.
⚠️----🔜----⚠️
# GMKTec Evo X-2 AI Mini PC ++ Ubuntu 25.10
Getting the Evo X-2 running on Ubuntu 25.XX (.10 at time of writing)
## Intro
I got an Evo X-2 to create a homelab local-LLM one-stop-shop (Ollama + Open-WebUI, eventually some image generation front-end, but out of energy for now). Had a lot of weird issues and caveats getting this up and running. So figured I'd put the commands used here in case anyone else runs into the same stuff.
## TODO
* Add breakout snippet for Ollama service entry edits
* Decide on image gen front-end / wrapper, install, troubleshoot, configure, update this
## Commands Ran
```bash
# Get Ubuntu up to Date & grab curl
sudo apt update
sudo apt upgrade
sudo apt install curl
# Enable SSH (todo: harden)
sudo systemctl enable ssh --now
# Install Claude Code CLI to help troubleshoot things
curl -fsSL https://claude.ai/install.sh | bash
# Install ROCM (I think this worked)
wget https://repo.radeon.com/amdgpu-install/7.1/ubuntu/noble/amdgpu-install_7.1.70100-1_all.deb
sudo apt install ./amdgpu-install_7.1.70100-1_all.deb
sudo apt update
sudo apt install python3-setuptools python3-wheel
sudo usermod -a -G render,video $LOGNAME
sudo apt install rocm
# Install pyenv & set Python 3.12 to global version
sudo apt install git && curl -fsSL https://pyenv.run | bash
pyenv install 3.12
pyenv global 3.12
python --version # verify
# Install packages necessary for python dev (these also prevent issues with Open WebUI)
sudo apt install -y build-essential libssl-dev zlib1g-dev libbz2-dev libreadline-dev libsqlite3-dev curl git libncursesw5-dev xz-utils tk-dev libxml2-dev libxmlsec1-dev libffi-dev liblzma-dev
# Install & Configure ollama service (todo: snippet of service entry)
curl -fsSL https://ollama.com/install.sh | sh
sudo systemctl edit ollama.service # set ollama to serve on 0.0.0.0
sudo systemctl daemon-reload && sudo systemctl restart ollama
systemctl enable ollama --now
systemctl status ollama
# Install open-webui (defaults to 0.0.0.0, no extra config necessary)
pip install open-webui
# Clean slate
sudo reboot now
```
# Dump-ster Diver
## Dump-ster Diver
[](https://www.docker.com/) [](https://www.python.org/) [](https://neo4j.com/) [](https://flask.palletsprojects.com/)
**A Knowledge Graph Forensics System for Document Analysis**
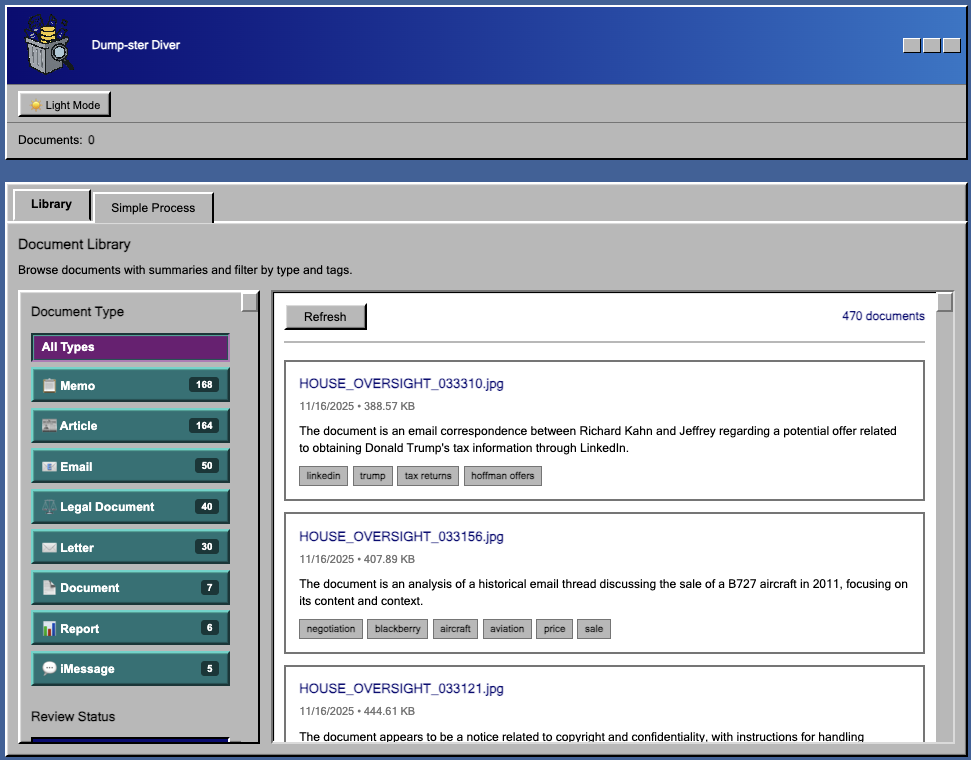
Dump-ster Diver is an AI-powered document analysis system that extracts entities, relationships, and insights from large document collections. This tool transforms unstructured documents into an interconnected knowledge graph, making it easier to discover patterns, connections, and key information across thousands of files - whether you're analyzing legal documents, corporate archives, email dumps, or any other large-scale document repository.
[View on Github](https://github.com/thebriandurham/dump-ster-diver)
### Features
#### 🎯 Processing Mode
**Simple Processing Mode** (Recommended for Large Collections)
* Generates concise 1-2 sentence summaries for each document
* Automatic document type classification (email, memo, legal-document, chat, etc.)
* Intelligent tag extraction for easy filtering and search
* Faster processing ideal for initial document review
* Review status tracking and flagging system
#### 📄 Supported Document Types
* **Text Files**: `.txt`
* **Images**: `.jpg`, `.jpeg`, `.png`, `.gif`, `.tif` (OCR via vision models)
#### 🎨 Interactive Web Interface
* **Windows 95-inspired retro UI** for nostalgia and clarity
* Filter documents by type, tags, review status, and flags
* Document detail viewer with inline text/image display
* Real-time processing progress monitoring
* Dark/light mode toggle
#### 🤖 Configurable AI Models
* Note: these are just what I used while testing this project
* **Text Models**: llama3.2:3b, qwen3:4b-instruct, qwen3:8b, qwen3:30b
* **Vision Models**: gemma3:4b, gemma3:12b, qwen3-vl:8b, qwen3-vl:32b
* Switch models on-the-fly through the UI
* Powered by [Ollama](https://ollama.ai/) for local, privacy-focused AI
#### 💾 Graph Database Storage
* Neo4j 5.13 with APOC plugins for advanced graph operations
* Efficient querying of entity relationships
* Built-in similarity relationships between documents
* Persistent storage with Docker volumes
***
# Image Caption
LLM-assisted screenshot captioning & renaming
## Image Caption
A Python tool that uses vision models through Ollama to automatically generate captions or rename images based on their content. Perfect for organizing screenshots and images with AI-powered descriptions.
[View on Github](https://github.com/thebriandurham/image-caption)
### Features
* **Caption Generation**: Automatically generates detailed text captions for images
* **Smart Renaming**: Renames images with descriptive filenames based on their content
* **Screenshot Focus**: Specifically designed to process screenshots, identifying applications, UI elements, and visible text
* **Error Handling**: Robust retry mechanism with error logging
* **Flexible Configuration**: Support for custom Ollama hosts and model selection
* **Batch Processing**: Processes all matching images in a directory automatically
# Nominal
My time in indie-dev-land
> Push buttons, flip switches, and race against the clock. Climb into the cockpit of an alternate history, 1960’s era spacecraft: the Odyssey. Challenge your critical thinking skills playing solo, or let your friends play as your Mission Control in an asymmetric game of crisis communication!
{% embed url="" %}
## About
Nominal was an indie, puzzle, asymmetric-co-op game created by yours truly under the "Offworld Systems LLC" brand. No longer available for purchase, but I still have all the source and binary releases. Reach out if you're curious. There's also copies and stolen keys floating around on the internet. I'll take that as a compliment
# Nanoparser
Python meets Azure Functions meets Azure MySQL.
{% embed url="" %}
## About
* Created an Azure MySQL database backend with an accompanying Azure Functions API to manage mining and payout information on the Nanominer ecosystem to better learn Azure services and automate pool mining administrative issues.
* Created a python script, nanoparser, to parse log files from Nanominer to ensure accurate share ratings when calculating payout ratios within a share nanopool pool.
* The data from nanoparser was uploaded to the Azure MySQL database through hardened Azure Functions.
## Postmortem
* Never go pool mining with your friends. They'll ask you to write code.
# Intel NUC Proxmox & Linode Homelab
Experimenting with baremetal meeting cloud virtualizatoin
## About
* Setup an INTEL NUC machine running Proxmox on baremetal.
* Hardened Proxmox installation and configured private subnets for virtualized hosts.
* Setup Linode OpenVPN instance, hardened the host, configured Linode Firewall rules, and setup private subnets for individual VPN profiles.
* Used OpenVPN host to secure communications between each virtualized host running on the Proxmox server.
* Configured a Kali virtual machine on the Proxmox server with an installation of Nessus and a secured/hardened remote desktop configuration to allow running vulnerability scans while away from home.
## Postmortem
* Learned a LOT doing this. But it also threw me down the `homelab` rabbit hole and now my wallet hates me.
# Active Directory Exploitation & Pivoting Lab
Attacking AD in a virtualized environment
## About
* Utilized VMWare Workstation Pro to setup an Active Directory environment to learn and practice AD enumeration, exploitation, and pivoting techniques.
* Setup a domain controller with group policy objects to emulate a real life, insecure Windows environment.
* Setup two vulnerable host machines and joined them to the AD domain.
* Used a Kali attack box to enumerate the AD environment, intercept and spoof NTLM traffic, and practice Kerberoasting and other common AD attack methods to compromise each host in the domain, as well as the domain controller.
## Postmortem
* A great, if time consuming, way to learn not just offensive security but AD admin skills.
* Protip: these 'about' sections are all pulled from the content of my previous site, and you can definitely tell I was writing *for* recruiters when I wrote this.
# TCM-Sec's Windows WiFi Extractor
Contributed to open source pentesting software
{% embed url="" %}
## About
* Contributed to TCM Security's development of their Windows WiFi Extractor tool.
* The program is designed to dump WiFi SSIDs and plaintext keys from Windows hosts utilizing the built-in netsh utility.
* Forked the original repo and converted the code to run in-memory only, as the original code created files (and therefore traces) on the victim computer.
* As a result: removed reliance on hard-coded integer accessors to parsed XML data and moved to a human-readable JSON format.
## Postmortem
* When you get excited to contribute to a cybersec superstar's repo because you see an obvious code optimization, don't forget to erase hard-coded sensitive information from testing prior to making a pull request... Whoops! 😬
# Rust Basics
You should learn Rust. No really, you should. It's great. I'm totally here on my own free will. Rust is definitely not watching.
{% embed url="" %}
## About
* Followed guided learning experience to get a better grasp of the Rust programming language so that I can make more performant offsec tools that can easily be compiled for various operating systems.
* Learned the foundations of Rust, including: using Cargo, data-types, error-handling, functions, control flows, etc.
* Created a single threaded web server to learn the basics of networking, sockets, and requests in the rust language.
## Postmortem
Ah, Rust. How do I love thee? Let me count the ways. But seriously, I do love Rust and this was a great intro to it. One day, when I'm not so busy, I'll actually go back and rewrite all of my old code in Rust. But, and I gotta say it, for now Python is my mainline for quickly whipping up tooling during engagements and for personal side projects.
# CTF Writeups
CTF Writeup Aggregation Post!
{% embed url="" %}
## About
Currently documented CTFS:
* Hack the Box - Business CTF 2022
* [Breakout](https://github.com/thebriandurham/CTFs/blob/main/HTB%20Biz%2022/Breakout.md)
* Challenge: A C2 implant's interface was left exposed on a victim's webserver. Break into the interface and enumerate its functionality.
* Compromised the C2 interface and extracted a non-native binary, 'bkd.'
* Performed analysis on the binary and extracted the flag from multiple strings present in the compiled code.
* [Chromeminer](https://github.com/thebriandurham/CTFs/blob/main/HTB%20Biz%2022/ChromeMiner.md)
* Challenge: A browser extension is believed to host cryptomining malware. Investigate.
* Downloaded and unzipped the .crx (browser extension) file.
* Reverse engineered heavily obfuscated malicious javascript code to retrieve the flag.
* [Lina's Invitation](https://github.com/thebriandurham/CTFs/blob/main/HTB%20Biz%2022/Lina's%20Invitation.md)
* Challenge: A CEO's password vault has been compromised after receiving an email with an attachment. Review the provided PCAP file and attachment to determine how he was compromised.
* Unzipped the attachment (a .docx file), used OLE Tools suite to analyze its contents, and discovered malicious VBA macros calling out to a fake Windows Update site and containing a part of the flag.
* Analyzed the provided PCAP file and found two indicators of compromised: a malicious HTML payload and some obfuscated PowerShell commands.
* De-obfuscated the malicious HTML payload to discover part of the flag.
* De-obfuscated and reverse-engineered the PowerShell payload to reveal the final part of the flag.
## Postmortem
Remember when you had time for CTFs? I remember when I had time for CTFs.
# Paratrooper
Your Pi in the Sky
{% embed url="" %}
## About
* Network enumeration script that is meant to be ran from a Raspberry Pi drop-box on a client's internal network.
* Stores the output of standard enumeration commands (such as ifconfig, netstat, etc.) and then uses scp to copy the enumerated data back to a listening host.
* Designed to be set up on a Kali instance and ran via Crontab to allow the script to execute on a set interval to ensure the data gets returned once a network connection is established.
## Postmortem
Oh the early, innocent days of my infosec obsessions. At least I was trying, right?
# DinoDisplay
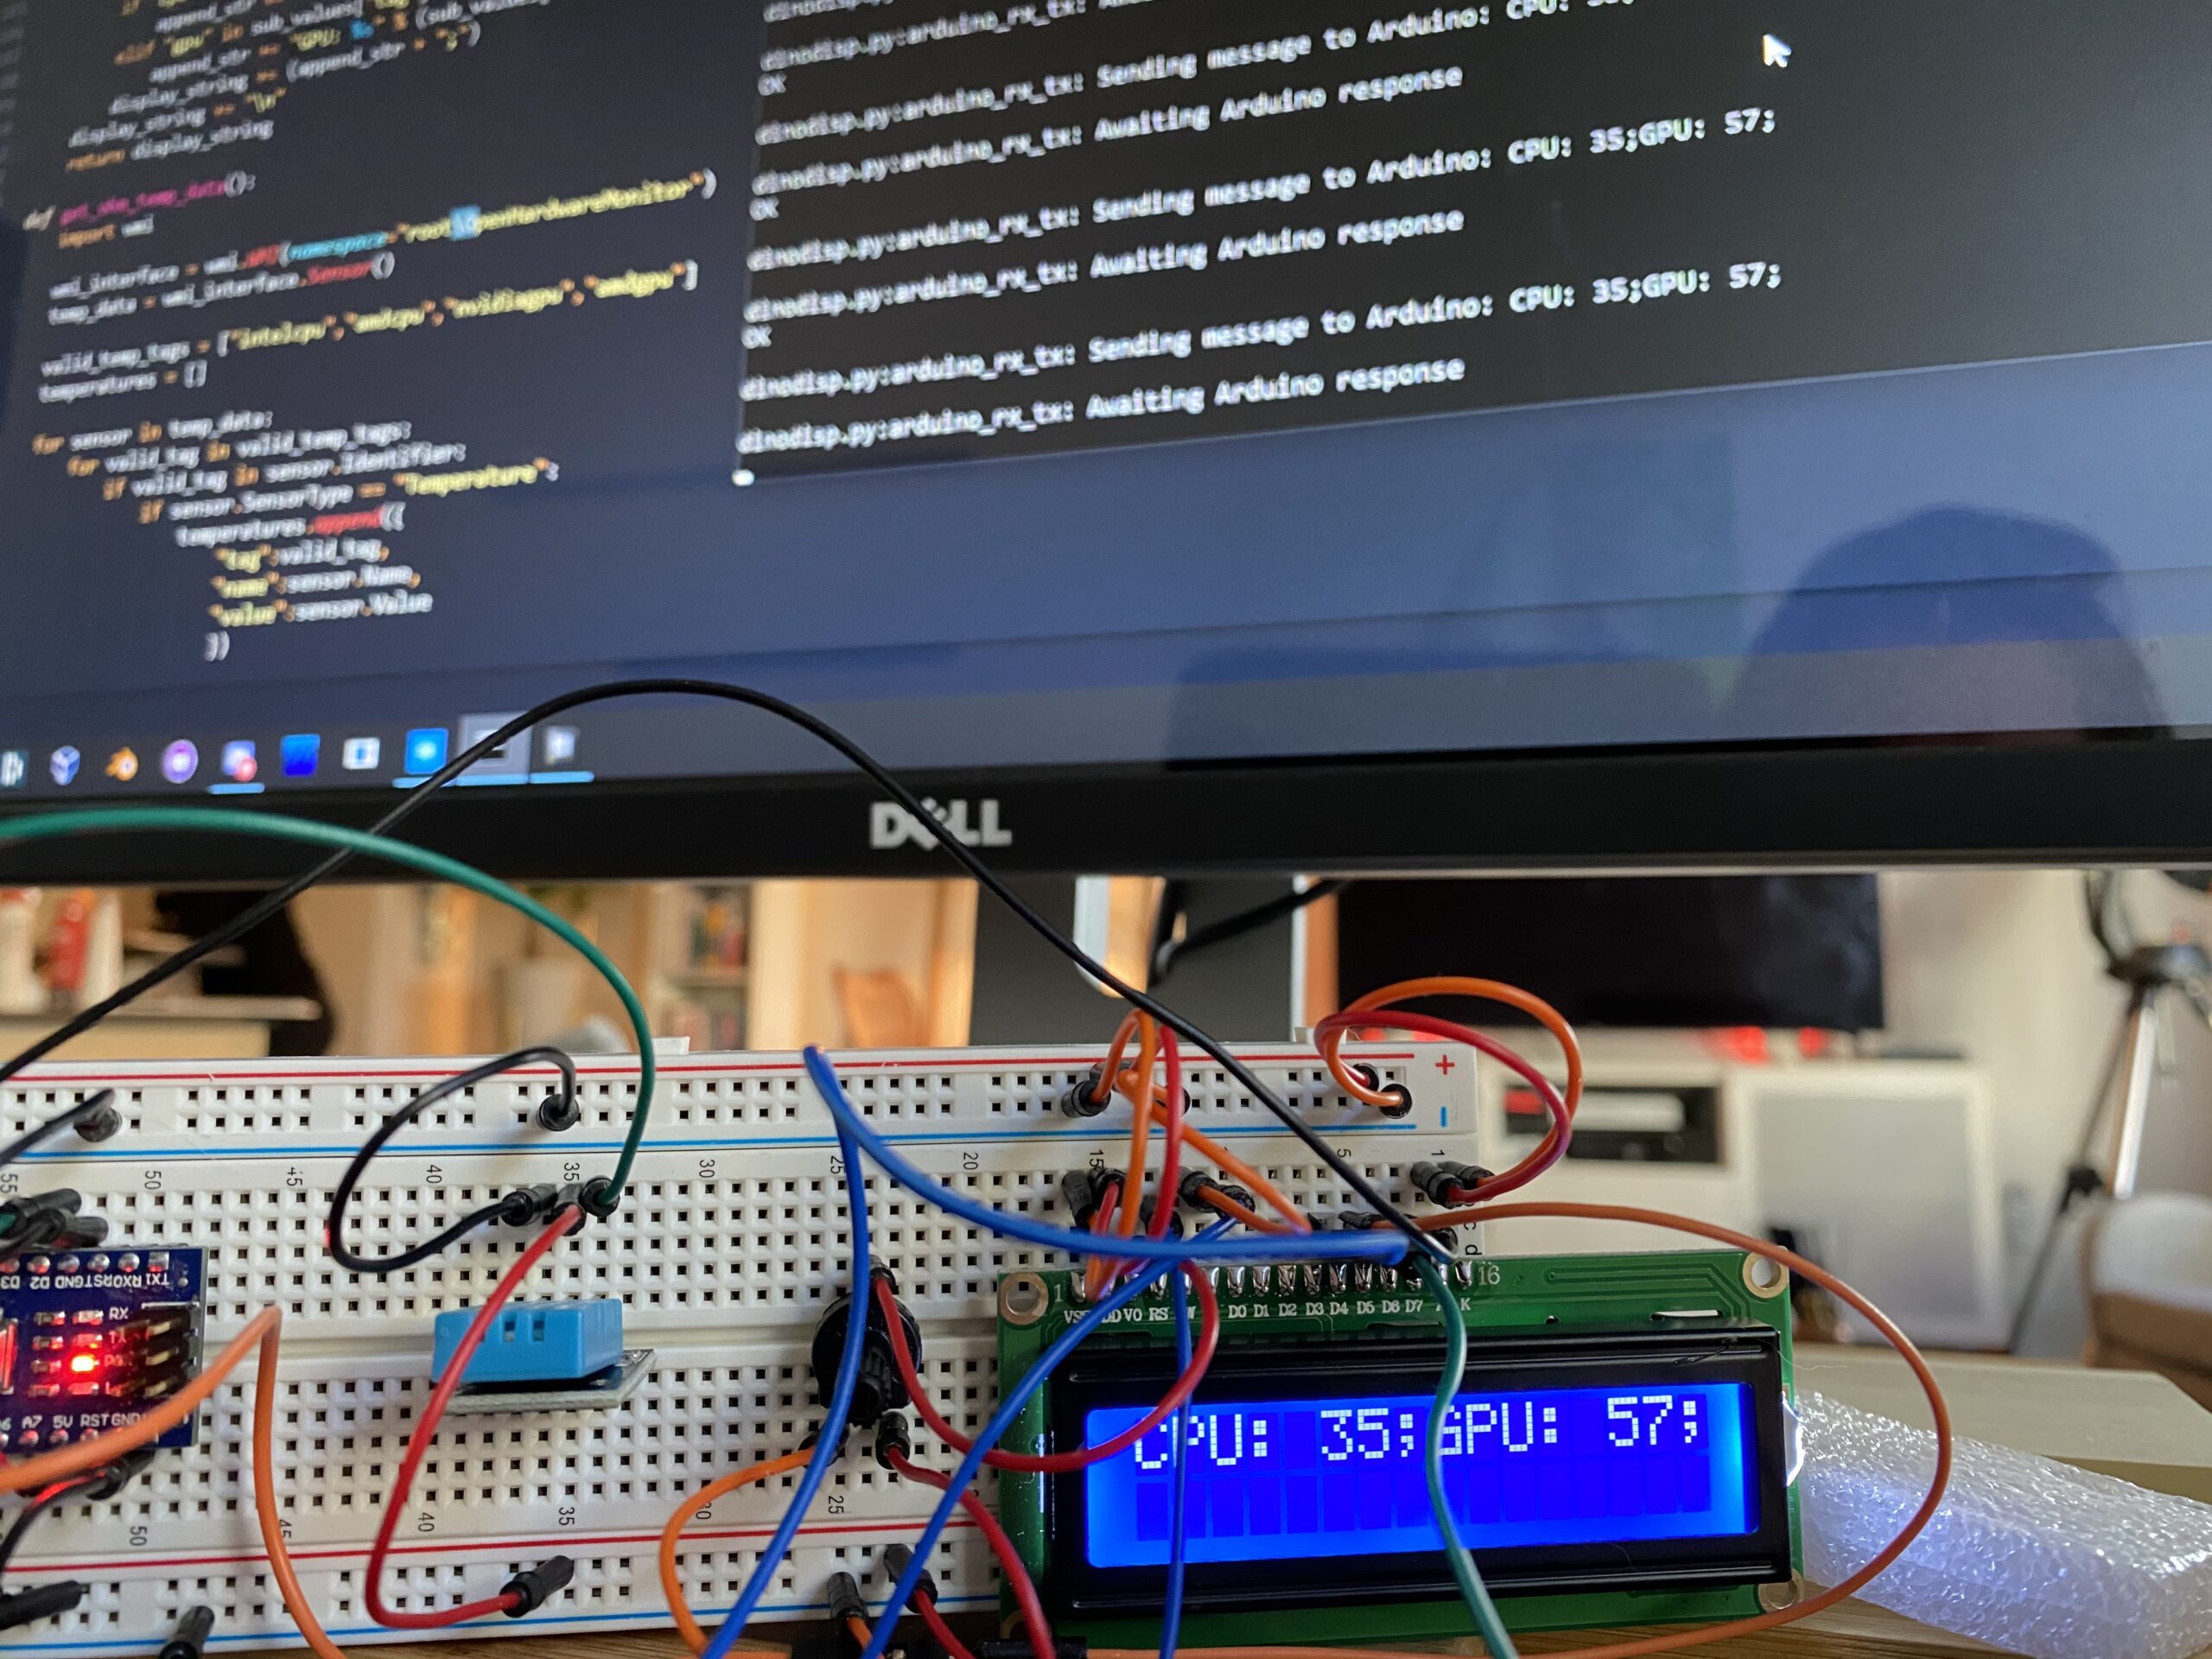
A little something to learn microcontroller to serial to OS-process communication.
Dino running on a breadboard setup
{% embed url="" %}
## About
* Created an Arduino-based PC hardware data display to learn serial communication between an arduino and a PC, as well as how to pull system information, such as CPU core temperatures.
* Utilizes WMI and Open Hardware monitor to fetch and provide said data to the arduino for display on a chosen screen solution (LCD/LED/etc.)
## Postmortem
* One of my first microcontroller -> serial projects. Cute!
# sqlcheck.py
You got your SQLi in my PCAP!
{% embed url="" %}
## About
* Python script that reads in a list of reserved SQL keywords and scans a provided input to determine whether or not a SQL keyword is present.
* Useful for PCAP analysis to determine the validity of SQLi security events.
## Postmortem
* Wrote this little diddy back in my SOC days. Shame I didn't think to also upload the required word list. Maybe I thought a simple list of SQL reserved words and symbols counted as proprietary info?